From control to intelligence: The next shift in risk management.
Thursday, November 19, 2026, 11am–12pm ET
Your institution may be completing risk assessments, monitoring controls, and reporting to the board on schedule. But how quickly would you recognize a material change in risk exposure between review cycles?
Risk functions face expanding mandates, fragmented information, and business conditions that move faster than traditional risk management processes. AI can accelerate existing work, but its greater opportunity is to change what risk teams can see, how quickly they recognize emerging threats, and whether insights reach the right decision-makers in time.
Protecht's Jared Siddle, a former Chief Risk Officer, will explore how North American banks, credit unions and financial services institutions can move beyond periodic risk assessments and point-in-time reporting to connected risk intelligence that helps the business recognize emerging risks, make better decisions, and act with greater confidence.
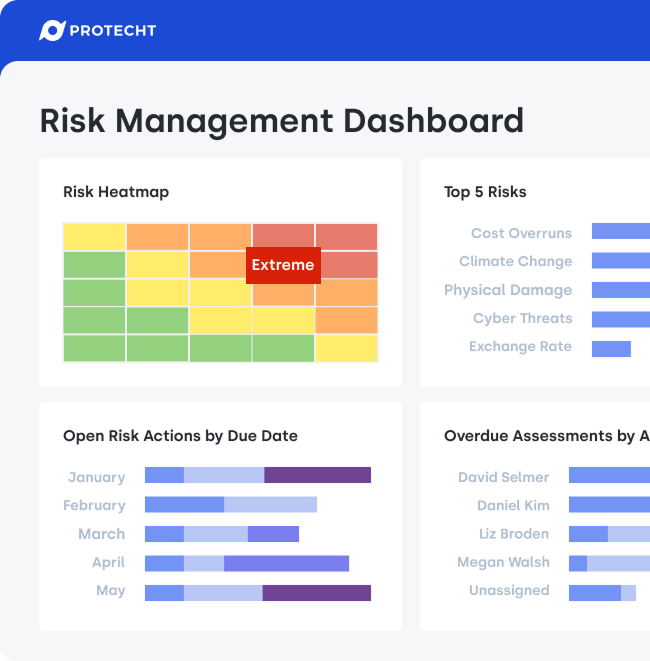
He'll introduce Protecht's six Risk in Motion processes, distinguish Control AI from Intelligence AI, and show how connected risk data, continuous monitoring, and third-party intelligence can help institutions recognize changing exposures and act sooner.
A practical view of continuous risk intelligence
Continuous intelligence doesn't replace periodic risk assessments or control testing. It builds on them by connecting risk information with changing conditions, helping institutions recognize material changes in exposure and respond without waiting for the next scheduled review.
Using practical banking risk scenarios, Jared will explore how internal risk and control data can connect with incidents, operational indicators, and external third-party signals to provide a more current view of exposure.
You'll also learn how to identify where the flow of information breaks down between an emerging risk signal and a management decision, and where improvements could make the greatest difference.
Guidance for your organization’s level of maturity
The principles apply whether you lead risk for a mid-tier bank with established governance structures or a credit union developing its risk management capabilities.
You'll learn how to make achievable improvements that strengthen risk visibility, decision-making, and business ownership, without needing the technology infrastructure or resources of a global institution.
The focus is on achievable improvements that strengthen visibility, decision-making and business ownership.
You will learn how to:
-
Distinguish between AI that accelerates existing risk processes and AI that delivers new insights into emerging risks.
-
Apply Protecht's six Risk in Motion processes to connect risk signals with timely decisions and actions.
-
Move beyond periodic assessments and reporting toward a more connected, continuously informed view of risk.
-
Recognize how connecting risk, control, incident, and third-party data can reveal changing exposures that isolated assessments may miss.
- Identify the most important gap between risk signals and action in your own institution, and practical steps to address it.
Your presenter
Jared Siddle
Jared Siddle is Protecht's VP of ERM Sales, North America. He is a Qualified Risk Director who has been Head of Risk Management at three different companies, including two of the world's largest asset managers. Jared has proven success in banking, fund management and other financial service companies across over 26 countries. He is passionate about governance, risk, compliance and sustainability. He is an expert at designing, developing, and executing customised enterprise-wide risk frameworks.
Your foundation for what comes next.
Protecht brings risk, compliance, controls, incidents, obligations, assurance and reporting together in one connected GRC platform.
Build a credible case by demonstrating immediate value while creating a scalable foundation for future transformation:
- Reduce manual work, duplicated systems and reporting effort
- Strengthen evidence trails and improve visibility across risk activities
- Quantify near-term value using measurable operational outcomes
- Expand into resilience, third-party risk, cyber risk and AI-enabled workflows