Skip to content

Governance, Risk & Compliance (GRC) Software

Connect governance, risk and compliance. Decide with confidence.


Book a demo       Watch a quick tour


G2-rating


Protecht brings risks, controls, obligations, incidents, audit, vendors, cyber and resilience together in one configurable, AI-enabled platform. Business teams, risk and compliance specialists, internal audit and the board work from the same information, so everyone can see what has changed and act on it.


CAPABILITIES
 

From disconnected tools to connected GRC.

Connected GRC means each risk, control, obligation, finding and action is recorded once and linked to everything it affects. That is what lets teams see the impact of a change and act on it together.

WHY PROTECHT

A trusted partner for connected GRC.  

USE CASES
 

What teams achieve with connected GRC. 

automate-workflows-icon

Replace spreadsheets and legacy GRC 

Move registers, history and relationships into one platform, with expert help on data migration, process design and phased delivery.

Read the transformation guide
empower-icon

Prove resilience to your executives, board and regulators 

Bring critical services, tolerances, vendors and test results into one view, with reporting aligned to DORA, APRA CPS 230 and PRA/FCA rules, whether they apply to you or you follow them as good practice.

See Protecht in action
icon-slideshow-1

Bring the business into GRC 

Let business owners complete risk assessments, attestations, incident reports and actions from one task list, on mobile or in Microsoft Teams, so risk management becomes part of everyday work.

See Protecht in action
new-features_icon-1

Stay ahead of regulatory change 

Turn alerts from content providers such as LexisNexis into impact assessments, owner actions and evidence linked to obligations and controls.

See Protecht in action
SOLUTIONS
 

Start where you need to. Connect the rest.

Every solution runs on the same platform and shares the same data, so you can begin with one GRC process and add others without starting again.

Enterprise risk management icon

Enterprise risk management 

Assess risks and controls, track KRIs and incidents, and report with confidence.

Learn more
Compliance management icon

Compliance management 

Manage obligations, regulatory change, attestations and breaches in one place.

Learn more
Controls management icon

Controls management 

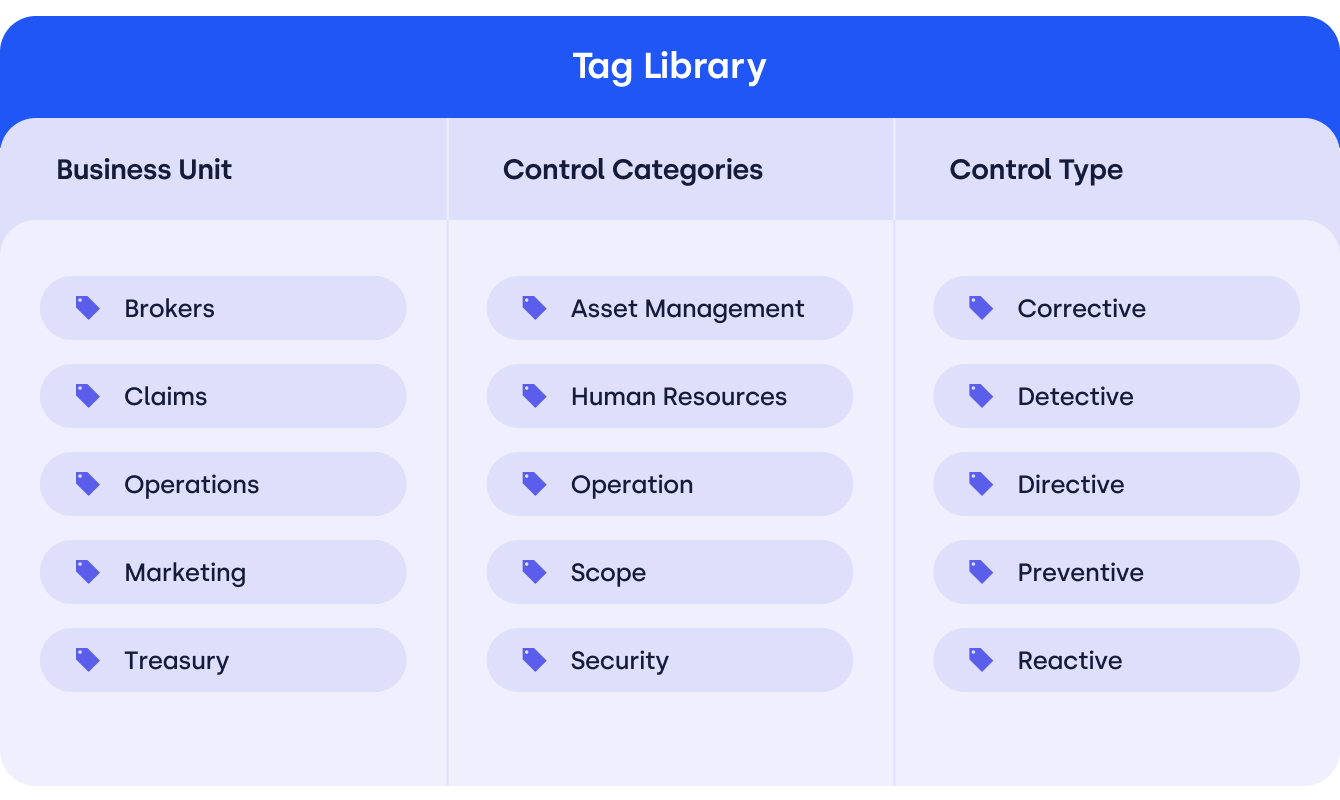
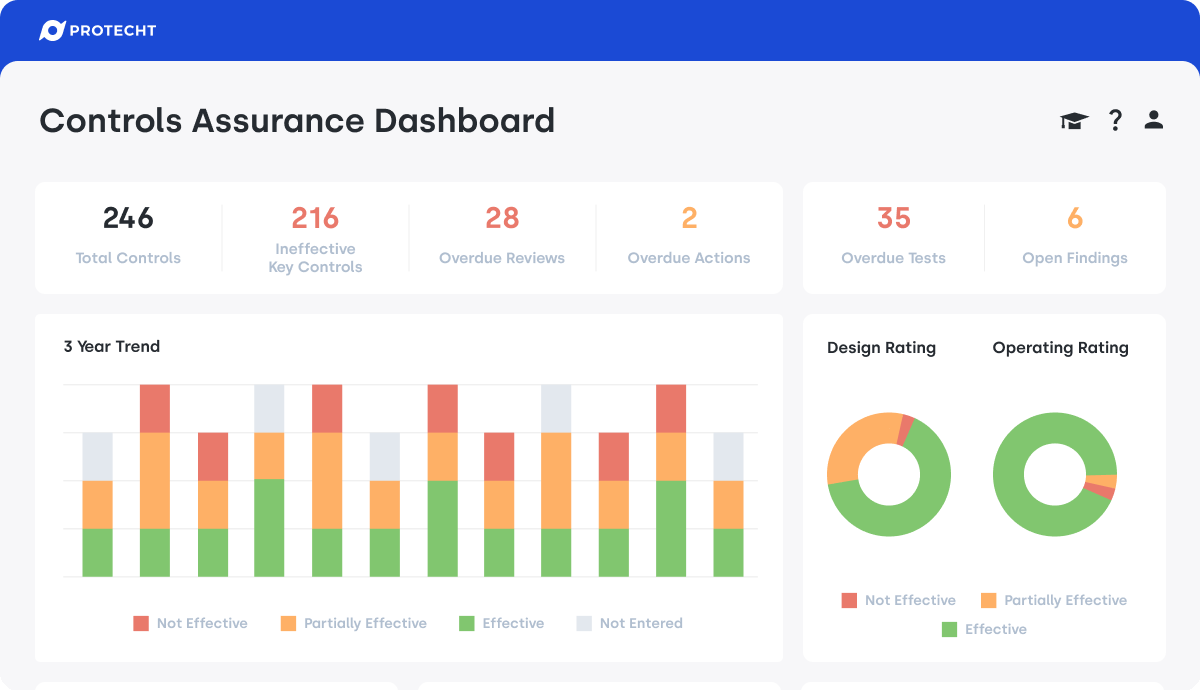
Design, test and assure controls from a single source of truth.

Learn more
Audit management icon

Audit management 

Run risk-based audits from audit universe to findings and reporting.

Learn more
Vendor risk management icon

Vendor risk management 

Onboard, assess and monitor third parties, with AI-assisted assessments.

Learn more
Cyber and IT risk icon

Cyber and IT risk 

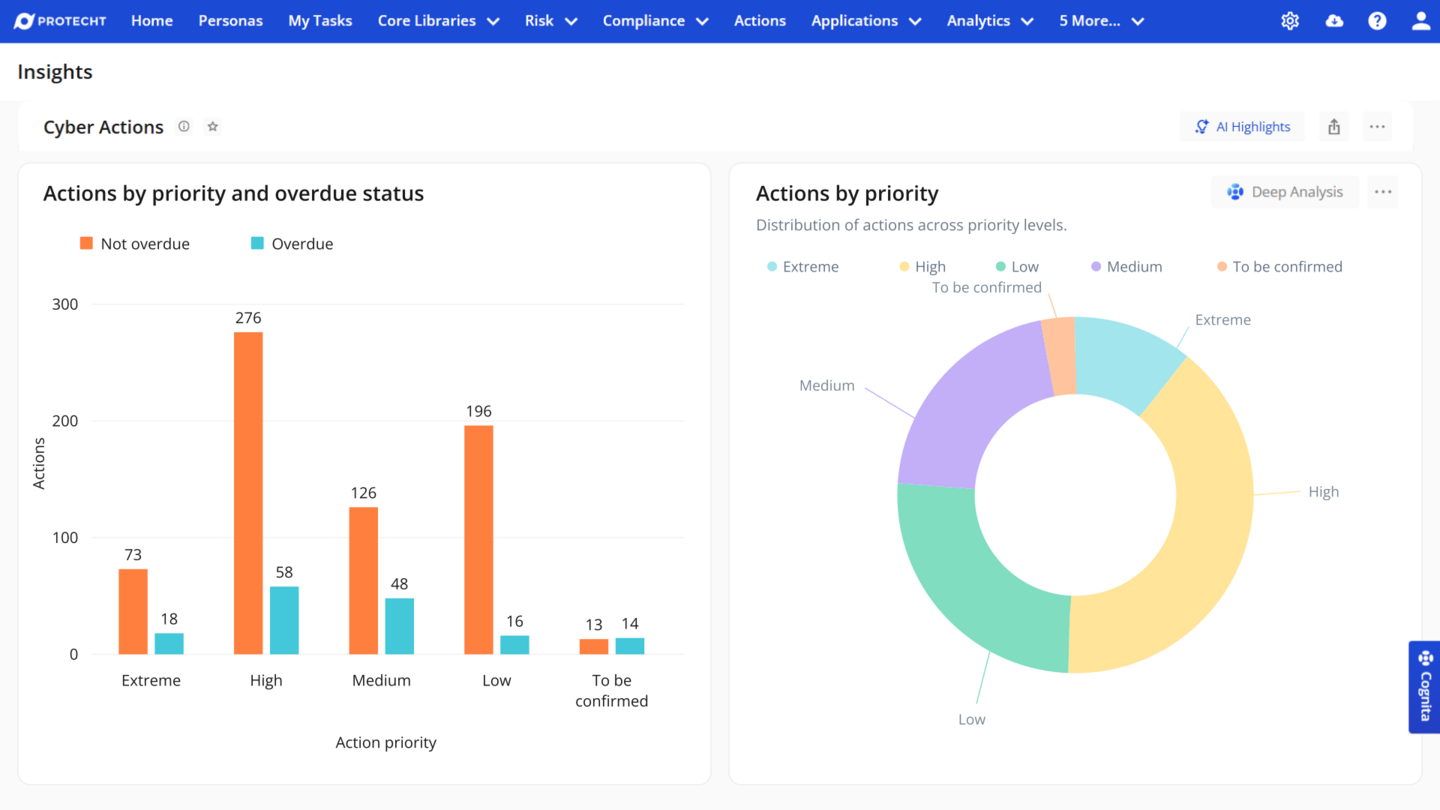
Connect cyber risks, assets, controls and incidents across frameworks.

Learn more
Operational resilience and BCM icon

Operational resilience and BCM 

Map critical services, set tolerances and test recovery.

Learn more
Workplace health and safety icon

Workplace health and safety 

Act on incidents and hazards, and build a culture of safety.

Learn more
 CASE STUDIES
 

How Impax built connected GRC on one platform.

Impax Asset Management started with incident management in Protecht to move beyond spreadsheets. It has since added audit tracking, operational resilience and information security on the same platform.

The result is one scalable system that supports efficiency, accountability and better decisions, from frontline workflows to board reporting.

"Our business is much more risk-aware now. Protecht has given senior management the ability to see what is happening within different business functions, and this in turn allows the C-suite to plan for the future using a risk lens."

John Bastow, Chief Compliance and Risk Officer, Impax Asset Management

See also: how Transurban replaced a legacy compliance system

Trusted by 200,000+ users across the globe

  • Afterpay
  • Aon
  • British Council
  • First Tech Federal Credit Union
  • Transurban
  • WorldRemit

INTEGRATIONS

Seamless integrations to power your GRC ecosystem.

Protecht connects GRC to the systems people already work in, so information stays current and nobody enters the same thing twice. Owners get reminders where they work, incidents and remediation move between teams, and reports draw on data from across the business.

For example: Microsoft Teams and Slack alerts for KRIs, attestations and overdue actions; ServiceNow and Jira for incidents and remediation; SharePoint for evidence; Power BI for reporting; Okta and Active Directory for access.

Thousands of ready-made app connectors mean many integrations can be set up without custom development, and our team helps design each end-to-end workflow.


Explore integrations

Risk Management Integrations
PRODUCT TOURS
 

See Protecht in action.

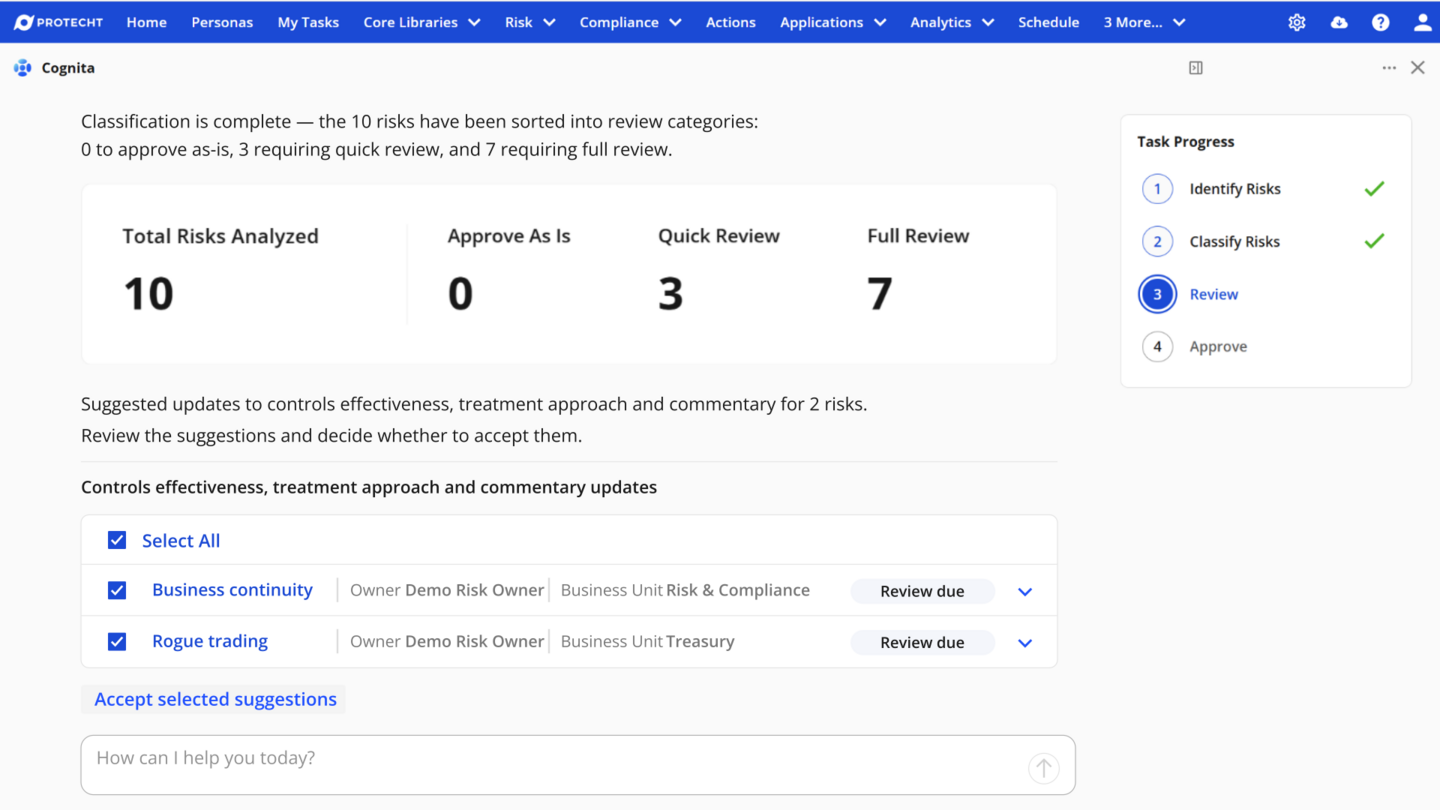
Watch how Protecht connects risks, controls, obligations, incidents and reporting in one platform, and how Cognita helps teams work faster.
 
Solving spreadsheet pain points with Protecht.


See why spreadsheets fall short for GRC and how one connected platform improves data quality, efficiency and collaboration.

 
Controls management in Protecht.


See how a central controls library, automated testing and a frameworks library connect controls to risks, obligations and incidents.

 
AI-powered report insights in Protecht.


See how Cognita turns scheduled dashboards and reports into structured, executive-ready insight.

FAQ

Get answers to commonly asked questions.

Learn what GRC software does, how Protecht supports governance, risk and compliance, and what to expect when you move to a connected platform.

Contact us
GRC software helps businesses manage governance, risk and compliance in one system rather than in separate spreadsheets and tools. It brings risks, controls, obligations, incidents, audits, actions and reporting together, so teams share one view of exposure and can show regulators and boards how risk is being managed.
Protecht covers the full GRC lifecycle on one platform: enterprise risk, compliance, policies and regulatory change, controls assurance, incidents, audit, vendor risk, cyber and IT risk, operational resilience and business continuity, workplace health and safety, and ESG. Each solution shares the same data, so a control, incident or finding is recorded once and linked everywhere it matters.
ERM software focuses on identifying, assessing and managing risk across the enterprise. GRC software connects that work with governance and compliance: policies, obligations, controls, assurance and accountability. The two overlap rather than compete, and Protecht supports enterprise risk management within a broader, connected GRC platform.
Protecht's AI, Cognita, is built into the platform to help teams capture, assess and understand risk. It guides users through incident logging, spots gaps in what they record, speeds up vendor assessments, writes summaries of scheduled reports and answers questions about your risk data in plain language. It is designed for safe use in GRC: people make every decision, AI-generated content is labelled, access follows role-based permissions, and data is encrypted and processed in isolated sessions. Learn more about Cognita.
Yes. Protecht's implementation team migrates your data during set-up and preserves the relationships between risks, controls and other records. Together you decide what to move, integrate, redesign or retire, so legacy workarounds are not carried over. Most customers start with one clear problem, such as incidents or risk assessments, prove it works end to end, then expand. Read the four decisions that shape a GRC migration.
Protecht helps businesses evidence compliance with frameworks and regulations including ISO 27001, ISO 22301, NIST CSF, SOC 2, SOX, DORA, APRA CPS 230, PRA/FCA operational resilience rules and FFIEC guidance. Controls can be mapped once to several frameworks, which cuts duplicated testing and evidence collection.
No. Protecht serves businesses from small teams to global enterprises with thousands of users. Smaller teams can start quickly with Marketplace templates and no-code configuration, then add solutions as their GRC needs grow.
Many customers go live within weeks, depending on scope and complexity. Marketplace templates, standard configurations and a structured onboarding process shorten set-up, and Protecht Academy trains users at every level.
Protecht holds ISO 27001 certification and a SOC 2 report. Data is hosted in your region in secure, certified facilities, encrypted in transit and at rest, and protected by role-based access, SSO and full audit trails.
Protecht pricing depends on your requirements, including the solutions you need, number of users, implementation scope and any integrations. The best way to get an accurate estimate is to speak with our team so we can understand your needs and recommend the right approach.


GET STARTED WITH PROTECHT

See GRC clearly. Act with confidence.

Meet one-on-one with a Protecht expert to: 

  • See how risk, compliance and assurance connect in one platform
  • Explore the solutions and use cases that matter to your business
  • Understand how to move from spreadsheets or legacy GRC
  • Get answers tailored to your GRC priorities

Join 200,000+ users who rely on Protecht to connect risk, compliance and assurance, and act with confidence. Book your demo today.  

G2-rating